Payment Processing for Prop Firms: Eligibility, Declines & Controls
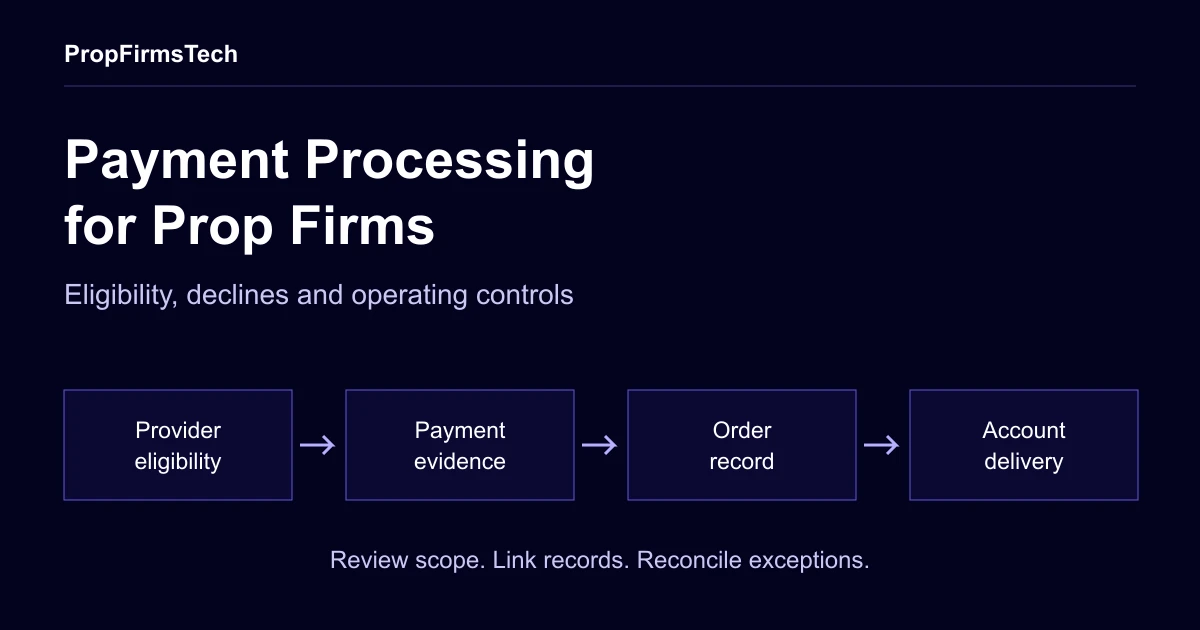
Payment processing for a prop firm starts with two checks: is the provider able to support the actual business, and can the operator reconcile each payment with the correct order and account? Adding another gateway does not resolve an eligibility restriction or an account-provisioning error.
A useful payment plan separates provider approval, checkout conversion, payment authorization, account delivery, refunds and trader rewards. Measure those stages independently before deciding which part needs work. This operator guide reviews primary provider documentation as of 31 October 2026; it does not describe a universal industry failure rate or guarantee a provider’s acceptance.
Check eligibility before choosing a gateway
Describe the business accurately: who sells the evaluation, what the customer receives, whether trading is simulated or live, how rewards work, the legal entity and countries involved, and any third parties handling funds. Give the provider the relevant customer terms and payment flows. Keep its decision and any conditions with the integration scope.
Policies must be checked provider by provider:
- Stripe: its prohibited and restricted businesses page, updated 22 September 2026, expressly lists funded prop trading among prohibited financial products and services. Do not treat it as a standard gateway recommendation for that category or assume a successful sandbox transaction establishes eligibility.
- PayPal: its acceptable-use policy identifies prohibited activities and categories requiring pre-approval. A customer’s ability to use a wallet does not establish permission for your business to accept payments through it.
- Adyen: its restricted/prohibited products list distinguishes merchant and platform/partner models and explains that additional restrictions may apply. Confirm the relevant model and onboarding requirements directly.
These are published provider-policy facts, not a determination of a particular entity’s legal position. Do not relabel a prohibited product, use another entity’s account or route around an eligibility decision. For providers that can support the disclosed business, confirm the approved services, countries, currencies and payment methods in writing.
Crypto, local transfer and regional payment options also need provider, entity, customer-country and method eligibility checks. They should be evaluated against the actual customer journey, reporting, refunds, fees and operational responsibilities rather than assumed to work everywhere.
Measure unique purchases separately from payment attempts
A customer may make several attempts for one order. Counting each attempt as a lost customer exaggerates the problem. Stripe’s decline guide recommends examining unique declines and excluding failed retries when analyzing authorization rates.
Define a reporting window and preserve stable order/payment references. The following is a proposed measurement framework, not measured PFT results or industry targets.
| Metric | Define the numerator and denominator | What it helps investigate |
|---|---|---|
| Checkout completion | Unique paid orders divided by unique eligible checkout starts | Customer journey, abandoned sessions and errors before payment submission |
| Payment authorization | Authorized eligible attempts divided by eligible submitted attempts, with retry/deduplication rules stated | Issuer, authentication, provider risk and integration outcomes |
| Account provisioning | Paid orders with the intended accessible account divided by paid orders requiring an account | Delivery delays, duplicate provisioning and missing records |
| Refund handling | Provider-confirmed refunds reconciled to the original order; pending/failed requests shown separately | Support backlog, account adjustments and financial exceptions |
| Disputes | Provider-defined dispute counts and ratios, with the exact eligible period and transaction population | Provider reporting and emerging operational issues |
Segment only where the data supports it: payment method, currency, customer country, device and acquisition source may reveal different issues. Keep the population and period comparable, and account for delayed or incomplete records. A raw failed-attempt count is not a revenue-loss estimate; some attempts are repeats, invalid or correctly blocked.
Diagnose the failure before choosing a recovery
Payment failures have different causes. Stripe distinguishes issuer declines, risk-blocked payments and invalid API calls. Its decline-code reference illustrates why recovery should follow the actual error and provider advice.
- Customer authentication required: offer the provider-supported authentication flow and handle a customer leaving or failing it.
- Issuer decline: display an appropriate customer message and use the provider’s permitted next step. The operator cannot force the issuer to authorize.
- Provider risk block: investigate the legitimate risk decision and configured rules. Sending the same transaction to another route is not automatically an appropriate recovery.
- Integration error: examine the request, configured product/currency and response handling. Changing the payment method may leave the implementation defect unresolved.
- Timeout or unknown outcome: check the original payment’s status before creating another charge. An uncertain response is not a confirmed decline.
Collect useful references and redacted diagnostics; never put full card data, credentials or identity documents into ordinary support logs. Apply the chosen provider’s access controls and data-handling rules.
Evaluate routing as an operating design
Multiple approved providers or payment methods may be useful when the business has distinct supported markets or needs. They also create more state, reconciliation and support work. Agree when a customer may choose another method, which provider advice permits a retry and how duplicate charges will be prevented.
For each route, document:
- The approved entity, business/service, market and payment method.
- The order reference and provider payment identifier.
- How pending, confirmed, declined, cancelled and unknown outcomes appear.
- Authentication and risk decisions that the route must respect.
- Retry/idempotency behaviour, event verification and reconciliation.
- Refund, settlement, reporting, fee and support responsibilities.
Stripe documents idempotent requests and webhook delivery behaviour, including duplicate delivery and event-order considerations. Those are provider-specific contracts; another provider’s guarantees and retry rules must be checked independently. A duplicate notification must not create another trading account or reward instruction.
Reconcile payment with account delivery
A successful browser redirect is not sufficient evidence of a confirmed payment. Join the provider record to the order, then confirm that the intended account exists and the trader can access it. Keep a recoverable state when the payment is confirmed but provisioning is delayed.
For a refund or adjustment, preserve the original payment reference, requested action, provider outcome and the corresponding access/affiliate changes. Decide who may approve the action and who investigates mismatches. The API integration checklist provides a record-ownership and exception-handling template; the CRM scorecard helps turn it into demo acceptance checks.
Trader reward obligations are a separate workflow from collecting fees and receiving processor settlements. A reward request, internal approval, payment instruction, provider outcome and recipient evidence are distinct. Use the payout reconciliation checklist rather than treating a dashboard’s “approved” label as proof of payment.
Reduce avoidable disputes with clear records
Keep the product, price/currency, billing identity, terms and refund/support process clear before purchase. Retain proportionate records of the customer’s agreement, account delivery and material support interactions. Stripe’s dispute-prevention guidance discusses clear policies and customer communication; neither guarantees that a dispute will be prevented or won.
Use the actual provider/network definitions for monitoring, deadlines and evidence. There is no universal chargeback threshold, win-rate target, refund fee or response-time promise established by this guide. A payment authentication or KYC step is not, on its own, a guarantee against fraud or a substitute for the operator’s obligations.
Security scope also depends on the architecture. A hosted or tokenized collection flow can reduce exposure to sensitive payment details, but compliance responsibilities still need to be assessed for the chosen integration. Stripe’s security guide describes that shared responsibility; this is not a claim that PFT or a customer’s whole business has a particular certification.
Prepare a payment-integration handover
Bring the approved provider scope, proposed customer journey, data/reference map, current reporting and example failures to the implementation discussion. Request a written test plan for confirmed/pending/declined payments, repeated events, delayed provisioning, refunds and reconciliation. Label examples as test data and obtain agreement before exercising live financial actions.
Compare setup, recurring, transaction, currency-conversion, refund/dispute, integration and support costs from current written terms. Use your own eligible cohort and test evidence to assess an improvement; do not substitute another firm’s headline percentage for your baseline.
Discuss payment gateway integration with PropFirmsTech to map the proposed connections and responsibilities. If changing an existing stack, include the migration guide’s reconciliation and cutover gates before agreeing a launch plan.