7 Red Flags When Choosing a Prop Firm Technology Provider
A useful red flag is a material requirement the supplier cannot explain, demonstrate or put in the agreed scope. Published prices, an attractive dashboard or a long feature list are not enough to evaluate a prop firm technology provider.
Start with your actual programmes, trading platforms, target markets and operating responsibilities. Then ask each shortlisted provider for comparable evidence. The seven checks below are proposed procurement guidance, reviewed 31 October 2026, not a ranking of suppliers or a claim that every firm needs the same architecture.
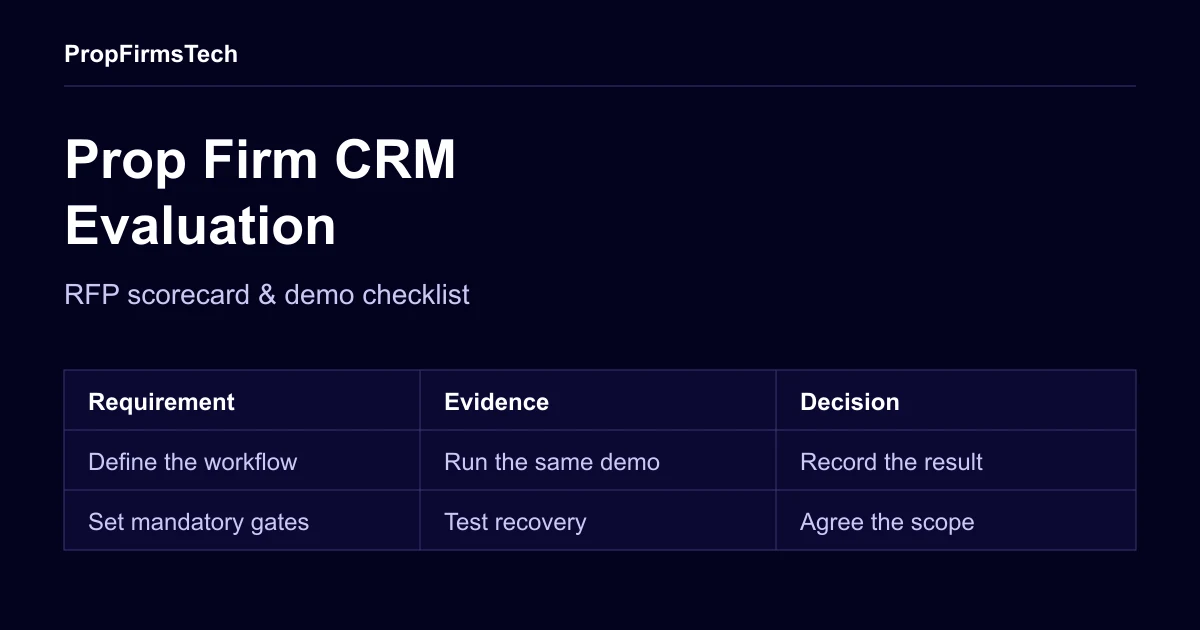
PropFirmsTech supplies prop firm software, so this is a commercial provider’s guide. Use the same requirements and acceptance checks when evaluating PFT. The CRM evaluation scorecard provides an editable way to record evidence, gaps and decisions.
1. A quote that leaves the operating scope undefined
A custom quote can be appropriate when platform access, integrations, account volumes or implementation work differ. The warning sign is an inability to explain what the quoted fee includes, what changes it and which dependencies remain outside the agreement.
Request setup, recurring, usage-based, revenue/profit-share and third-party costs separately. Define what “active account” means if it affects billing: an evaluation account, funded-stage account, archived record and reset may be treated differently. Compare the same expected configuration and volume, including support, exports and exit assistance.
A flat fee, account-based licence or managed revenue-share model can include different responsibilities. Compare their scope and cost under stated scenarios instead of assuming one structure is always cheaper or better. The UK government’s Sourcing Playbook discusses whole-life cost and service-specific evaluation; those are useful planning principles, not a statement that private prop firms are bound by UK public procurement rules.
Evidence to request: a dated scope and cost schedule with inclusions, exclusions, assumptions, change-control terms and termination obligations. Do not rely on an old comparison article for current competitor pricing.
2. Rule behaviour that cannot be demonstrated
“Risk management included” does not tell you how an account is evaluated. Write down your own rule definitions, then inspect the configured calculation and trader display together.
Include the balance/equity basis, open profit/loss, commission treatment, reset timezone, rounding, phase transitions and what happens when data is delayed. If you offer different evaluation or Instant Funding programmes, distinguish their rules and account actions. Do not assume every programme has the same phases or reward conditions.
Test with agreed synthetic scenarios: a daily reset with an open position, a loss-limit boundary, a completed phase and a delayed update. Record which system makes the decision and how an operator reviews an exception.
Evidence to request: a versioned rule definition, matching test results and a traceable account-status change. Product-specific official documentation, such as Match-Trader’s challenge configuration, can help frame questions without establishing the behaviour of another provider’s implementation.
3. Integration claims without access and recovery details
A platform logo or the words “API available” do not establish that your required actions are supported. Confirm the actual interface, version, permissions, environment, limits and maintenance owner for each connection.
Ask the provider to follow a confirmed order into one accessible account. Then examine a repeated event, a timeout and a missing update. How is an uncertain outcome reconciled? Who can replay or correct it? The API integration checklist covers these contracts and ownership questions.
Provider APIs can serve different users and purposes. cTrader Open API describes trading-account access; that does not automatically establish operator administration rights. TradeLocker distinguishes Brand and Public APIs. Request the access needed for your workflow rather than treating those interfaces as interchangeable.
Evidence to request: a documented integration contract, permitted access and a test/reconciliation log. A manual approval may be intentional; the concern is an undisclosed manual dependency or an unrecoverable failure.
4. Permissions and audit records that stop at the interface
A hidden button is not proof that an action is restricted. Define which roles can change programmes, alter account access, approve a reward, issue an adjustment and export customer data. Confirm the same restrictions apply to direct requests and relevant APIs.
OWASP’s guidance on object-level authorization explains why permission checks must protect the specific object and action. In a provider-approved test environment, ask to see an authorized action and a forbidden attempt against an account outside the test user’s permitted scope.
Agree what audit records identify the actor, action, time and affected record, including corrections. Ask who can retrieve those records and how long they are available under the agreement. These are requirements to verify, not claims that a particular PFT deployment has passed a security assessment.
Evidence to request: a role/action matrix and redacted permitted/denied test results with corresponding audit events. Do not test a third party’s live customer records without authorization.
5. Support promises without an escalation process
“24/7 support” and a response-time headline need definitions. Ask which incidents are covered, when the clock starts, what counts as a response and which team owns a platform, payment-provider or integration incident.
Distinguish acknowledgement, diagnosis, workaround and resolution. Agree severity levels, escalation contacts, communication cadence and the evidence needed for investigation. If an external provider controls the failure, identify the handover and who keeps the operator informed.
Review a sample incident runbook or an approved redacted incident record. A sales team’s quick reply alone does not prove production response performance, and a longer implementation timeline alone does not prove the software is unready.
Evidence to request: scoped service/support terms, an escalation path and a rehearsal using a hypothetical incident. Avoid importing another provider’s advertised average into your own contract expectations.
6. Data export and migration left until termination
Ask how your records can be exported before choosing a system. Include trader/account identifiers, programme history, orders, refunds, rewards, affiliate adjustments and the audit or identity-verification records you are entitled to retain. Confirm permissions, formats, history coverage, cost and exit assistance.
A migration promise needs acceptance gates. Agree mapping, a staging import, count/value reconciliation, exceptions, cutover and rollback responsibility. A successful import request is not proof that history and balances reconciled. Use the migration guide to plan those checks.
A single-platform deployment can be a deliberate choice, and a multi-platform offer still needs tested integrations. Evaluate the business dependency, contract/access terms and exit options. Do not assume a number of supported platform logos provides continuity or identical rule behaviour.
Evidence to request: an actual supported export sample and a written migration/exit plan. No universal switching-cost multiple or zero-downtime result is established here.
7. Proof that cannot be attributed or reproduced
Customer logos, retention percentages, fraud claims and performance statistics need context. Ask whether the customer has approved the reference, which service was used, what period was measured and how the result was calculated. A testimonial’s presence is not independent verification of its numbers.
For a case study, distinguish an operational result, such as fewer unresolved provisioning exceptions, from revenue growth. Record baseline, intervention, denominator, period and other changes that may have influenced the outcome. Ask what failed or was excluded as well as what improved.
For fraud or rule monitoring, verify the specific supported checks and human-review process rather than assuming all strategies, multiple accounts or disputed payments represent misconduct. Your published programme terms and evidence should govern decisions.
Evidence to request: permissioned references, source-backed case data and a demo relevant to your programmes. Unsupported industry statistics or unattributed promises should not be used as a substitute for product evidence.
Record a decision, not just a feature checklist
Keep each critical requirement, evidence link, outstanding dependency, owner and acceptance decision together. A proposed handover can be as simple as:
| Requirement | Evidence to collect | Decision before signing |
|---|---|---|
| Commercial scope | Dated quote and cost assumptions | Included, optional, excluded or unresolved |
| Rule/account workflow | Agreed scenario and traceable result | Accepted, correction required or not demonstrated |
| Integration and permissions | Access contract, recovery and role tests | Confirmed scope and responsible owner |
| Support | Severity/escalation terms and incident exercise | Coverage and unresolved dependencies |
| Data exit | Supported export and reconciliation plan | Portable records, costs and acceptance gates |
Apply mandatory gates before comparing optional features. Record unknowns as unknowns rather than scoring them as working capabilities. Resolve conflicts between the demo, contract and public copy in writing.
Book a PropFirmsTech demo with your requirements and use the CRM scorecard to review our proposed scope. If payments or rewards are part of the brief, include the payment operations guide and payout reconciliation checklist. The useful outcome is an agreed, testable implementation and operating plan.